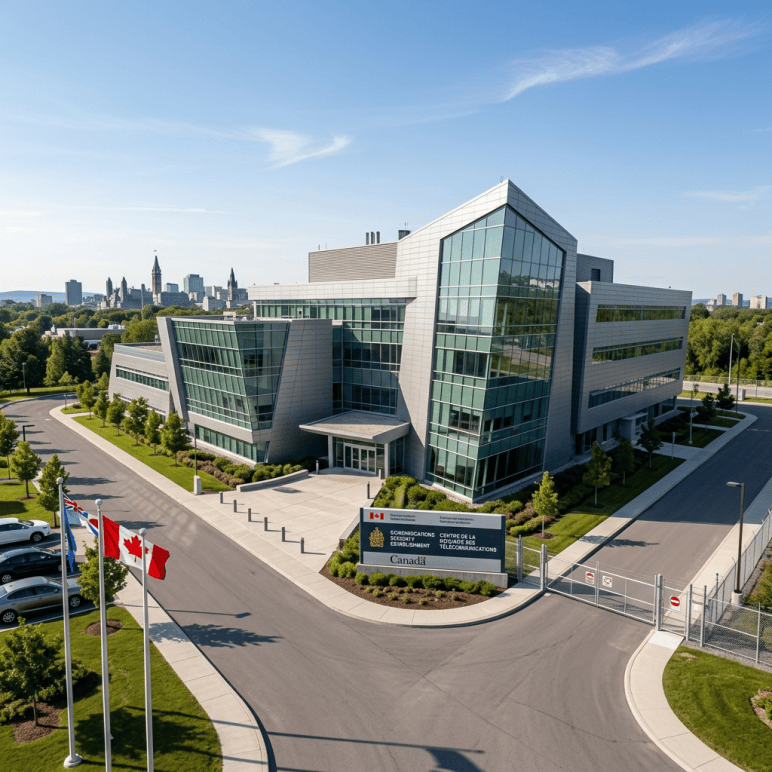
The Communications Security Establishment

Humanoid robot viewing holographic neural reflection analysis in laboratory

As promised in the last blog and in the spirit of looking at the two agencies responsible for intelligence and counter intelligence in Canada, we now turn to the Communications Security Establishment (CSE). With 3,232 employees, this “cryptologic” agency is about the size of CSIS, which we last wrote about, but it has a slightly larger budget of $948 million (2022/23). If CSIS prides itself on its emphasis on privacy and secrecy the CSE with also a serious level of investigative powers, seems to be the very poster child for staying hidden.

This agency does not report to the Minister of Public Safety but rather to the Minister of Defence. There are also two sub-agencies which fall under the CSE umbrella; the Canadian Centre for Cyber Security and the Cyber Emergency Response Team. Simply put this group’s job is to supply the “Government of Canada with information technology security and foreign signals intelligence”.

One significant difference between CSIS and CSE is the fact that they have somewhat different operational targets. Established in 2019 the CSE Act established that the CSE could not “target Canadians or anyone in Canada, interfere with the course of Justice, or interfere in the course of democracy”. They are there to be “defensive” and counter the cyber threats which may threaten such things as the energy grid, telecoms, health care databases and the “elections infrastructure”. They are also there to target foreign terrorist groups, cyber criminals, and state sponsored hackers. Their operations are divided into two parts, the second part being to gather foreign intelligence through signals intelligence (SIGINT) which involves the “interception, decoding and analysis of communications.” When signals intelligence started in the 1900’s it was basic and involved the interception of radio and telegraph transmissions. In 2026 with the advancement of technologies, we are now talking about the interception of text messages, phone calls, and computer and satellite traffic.

Furthermore there is a research directorate inside the agency, partly made up of the Tutte Institute for Mathematics and Computing (named after Dr William Tutte, a codebreaker and mathematician credited with breaking the Lorenz code during WWII).

This type of mandate requires a different candidate for the job and their recruiting initiatives focus on mathematicians, computer scientists and engineers. A prospective employee such as a mathematician needs to be familiar with cryptography, number theory, linear algebra, and data mining. Starting salary, in case you are thinking of applying is $78,000 but can go up to $178, 000.They do also advertise a generous maternity allowance of 93% of pay.

The CSE is currently headed by Caroline Xavier. She is a thirty year Federal servant having worked in several different departments, usually with an emphasis on IT and infrastructure. She also served in the Privy council office for three years as an assistant to the Cabinet, Security and Intelligence from 2017-2020. It would be fair to say that she comes from the more political arm of the government than a long term hacker investigator. There should be no mistake that like every Federal government department, throughout their annual report there is the obligatory references to “integration”, “working together” and “working with our partners”, and providing “timely guidance”.

Armed with my high school calculus, this is indeed a world outside my realm of comfort and expertise, but it is a field that with the advancements in Aritificial Intelligence (AI) and Machine Learning (ML) quickly developing into a most pressing need. It is on the conscience of all the world powers and the Five Eyes group in particular. Because it is part of the Defence department in Canada, CSE is also now an agency which has received or is receiving greater funds going forward under the current Liberal government, having been pressed to raise defence spending up to 5% of GDP. In its 2026 annual report, they confirm that they are in the process of increasing their work force by 8.1% for a total of 4,178 employees.

In that same annual report, in an effort to try and gauge a level of CSE success or effectiveness, we are pointed to case studies where numbers are thrown at you, but as a layman they are quite meaningless and obscure to the point the level of the CSE response or involvement in any singular investigation can not be determined. The organization says that they handled 14,700 “general inquiries”; that they responded to 3,216 cyber incidents of which 2,252 they notified the organization and “provided support”; and they sent out 97,000 security alerts to 1363 subscribers. Under the foreign signals intelligence banner they said they also sent out 3,926 “foreign reports”. All meaningless and indisputable but clearly designed to be impressive.

The CSE relies on Ministerial authorizations to conduct foreign cyber operations and in 2026 they were given 13 of these authorizations. Again, little is said about what these operations involved. One being the exposure and curtailment of a large “phishing” campaign which had targeted Federal institutions. The second they allude to is the countering of a Ransomware as a service (RaaS) cybercrime group.

They speak of their Communicatons Operational Production and Co-ordination Centre which runs 24/7 with cooperation from the Five Eyes and other “Federal partners”. The CSE in justifying their all night shifts say that there were 121 cyber security “incidents after hours”(I would have assumed that an organization such as this would have to be open for business 24 hours a day); and that they “co-ordinated response to 220 significant terrorist or global incidents this year”. When reading this document it always seems to raise the question as to whether the CSE is more an information funnelling operation or a pro-active cyber community.

Unfortunately it is difficult to measure their effectiveness when there is little to compare. The counterparts to CSE is the National Security Agency (NSA) in the U.S. and the GCHQ in the United Kingdom. But they are unfair comparisons, much like comparing CSIS to the CIA. Whether Canadians want to believe it or not, Americans and the Brits, are playing in the NHL of the spy world, Canada and its agencies are in the lower tiers of Junior hockey. For instance the NSA has 32,000 employees and its budget in 2013 was around $14 billion. Thanks to the exposure by Edward Snowden, we learned that at that time, the NSA was intercepting and storing information on over 1 billion people, and just through cell phone technologies were tracking hundreds of millions of people.

The CSE is structured and set up like an NSA, but the capabilities and reach of the organizations is pointless. Apples and oranges. One suspects that much that is reported and utilized by the CSE originates from these much larger and offensive orientated agencies.In the eighties as a point of interest, when I was with Security Service, even then, the Americans didn’t trust the Canadians because of our socialist leaning governments. Nevertheless there is a level of cooperation, and the CSE points to “Salt typhoon” which targeted the networks as one where they worked with CSIS, the FBI, and NSA.

When some criticism raised to the surface and became public, it inevitably was because “inadvertently” CSE had collected information on Canadians which was originally gathered or utilized from foreign intelligence agencies. They also got caught improperly sharing data on Canadians to international partners. Personally the idea that CSE cannot target Canadians, while CSIS can makes little to no sense. If Canadians are wrapped up in intelligence gathering or sharing with the enemy, should they expect to be safeguarded from scrutiny of CSE? The CIA works with the NSA and have no such allusions.

The problem I see with both CSE and CSIS is the rather weak looking and arbitrary screening of their activities. Maybe it is living in this era of often weak kneed and woke sycophants to a Federal government which makes me suspect of what is being monitored and which targeting is being approved. Admittedly the Federal government’s reaction to the trucker convoy and the declaration of the Emergencies Act has shaken my confidence. The revelations of Snowden in the U.S. also shook my once solid belief in patriotic efforts when left in the hands of the unscrupulous politicos when I expected better. It should be noted that the Snowden revelations were front and centre and part of the era of both the Bush and Obama presidencies. So it is a dilemma.

I admired the American efforts in finding Bin Laden, but that trust gets usurped by then learning of the random collection of once thought to be considered private information of its own innocent citizens. We need these agencies, but control of their technological powers clearly needs to be harnessed and they need to be to assure us that they can distinguish the enemy from the innocent. In Canada can this be done by a handful of Parliamentarians whose first loyalty is to their political stripe?

In many ways we are living in ominous times brought about by rapid advancements in the same technologies that could also do unbelievable good. Do we leave it NVIDIA, Google, or Meta to decide where the power is utilized and then in turn provided or sold to groups like CSE? Big questions, few answers coming from our governments, as we are forever told to be content with trusting in our Federal institutions. It is a big ask.

I Spy….

Photographer in a beanie holding a camera and carrying a case in a cobblestone alley

There are two agencies in Canada which go largely ignored, but fall under the various branches of enforcement. This is mainly due to the fact that both agencies, the Canadian Security and Intelligence Service (CSIS) and the Communication Security Establishment (CSE) live and exist under a veil of secrecy. This is not by choice, their very mandate is to stay hidden, out of sight of the “enemy” and therefore equally out of sight of any prying Canadians who might be interested in seeing or measuring their value and effectiveness.

Both of these agencies are research and intelligence based organizations, so it is somewhat misleading to put them in the category of “investigative” units like the RCMP, or some other operational policing unit. They are less hands on and often dependent on other agencies to carry on the investigation when their gleaned intelligence traverses over into the criminal element. Also, one needs to remember that these are strictly “political” agencies, the enemies or their targets of their investigations are purely determined by the political powers of the day. So targeting can sometimes be confusing. Case history shows us that one person’s defined terrorist has the possibility of being tomorrow’s favoured politician. The examples are many; Yasser Arafat and the PLO, Sinn Fein and the IRA are a couple which come to mind, both leading terrorist organizations whose leaders then became favoured politicians. In Canada, think of the truck convoy protesters in Ottawa honking their horns and the Liberals then requesting that all Federal resources be joined into an investigation of them, including CSIS.

This is just to point out that when investigational mandates intertwine with elected politicians, even those that believe in the necessity of an organization such as CSIS, it is also agreed, that the line between legitimate targeting and Orwellian nightmares is a fine one. Therefore in the case of agencies such as CSIS, in order to maintain democratic freedoms, substantial oversight is needed to be put in place. This need coupled with the current level of claimed security and investigational privacy, in the CSIS case, the public is kept distant from any investigative results and instead we must rely on government committees and the like to oversee their investigations. The dilemma in other words is that the government that decides the targeting also oversees the agency doing the targeting.

In this post blog we are looking at CSIS, whose mandate is about as broad based and as open to interpretation as any existing in government. Section 12 (1) of the Act states that the mandate is to reduce “threats to the security of Canada” and tells them that they “may take measures, within or outside of Canada, to reduce the threat”. Of course there is an obvious problem when the language is so generalized as to be useless. What constitutes a “threat” and what are the “measures” that are available? The authors of the Act do try and define it further without much success by saying “the measures should be proportional in the circumstances, having regard to the nature of the threat”. No kidding. Furthermore, the Act says that before any undertaking they are counselled to “consult, as appropriate, with other Federal departments, or other agencies as to whether they are in a position to reduce the threat”. A second rather obvious directive.

Besides the gathering of “intelligence”, a very large part of the CSIS mandate is the conducting of security screenings of individuals entering Canada, or wanting to enter Canada, as well as the screening of persons under any of the current government programs. CSIS says that in 2025 they conducted 129,000 government related security screenings and over 438,600 immigration and citizenship referrals. There is no easy public measure of how effective those screenings are or how in depth and there have recently been a couple of stories which would indicate that the screenings are not foolproof, but it is very difficult to measure when looking from the outside in.

In terms of full disclosure, I was in the RCMP Security Service, the precursor for CSIS from about 1981 to 1984. Although asked to go to the new agency, I chose to return to criminal work. CSIS decided to go ahead without me and officially began in 1984; so it now haves a 40 year history, and has gone on with little or no outside mention or attention by the average member of the general public. Clearly it is easier to avoid controversy if one is allowed to never speak.

Despite this general need and application of secrecy, there have been two reports which recently came into public, or at least my view. One was by the Journal of Police and Criminal Psychology which examined the current plight of workers within CSIS. This was after receiving complaints from within the agency, who according to the complainants, were working in an environment “laden with stigma”. So in 2024 the study conducted interviews of 38 employees ranging in age from 31 to 64 years old. Of those interviewed 48% were female and 52% male. This is actually a statistically very small sample, as there are currently 3,367 employees in CSIS.

As an aside, for the record, those employees make up $493 million in salaries and have an additional $320 million in operating expenses. The CSIS overall budget therefore totals $813 million. The salary range for a CSIS intelligence officer is from $87,000 to $120,000. The head of the unit is Daniel Roger who has a salary of somewhere between $230,000 and $270,00 and sits at the executive level of a Deputy Minister.

So this is not a small agency but it is not a large agency either. As a comparison the RCMP have about 6,000 employees in British Columbia alone. The Journal study and the lead researcher, Rosemary Ricciardelli, from her inquiries discovered that the biggest problem for morale in the Service was the fact that the employees were “getting no recognition for what they do”. That they work in a field which is “exposed to potentially, physically or socially traumatic events”. As a result fewer than half of the employees interviewed “recommended working there.”

The first part of the finding leaves me a little apoplectic. Apparently we are led to believe that employees who joined and signed on to be part of a “spy ” agency didn’t think that their required duties and assignments needed to be kept secret? Do they feel neglected in not being able to take selfies at their work places or put video on Instagram showing “a day in the life of a spy”. Mind boggling.

As to the second part of being exposed to traumatic events, once again, what did they think the job involved? I would agree however that exposure to the day to day violence around the world would be at times heart breaking and possibly lead to depression and anxiety. And I would also agree that some sort of psychological counselling around this issue should be a permanent part of the protocol inside the agency. However those that are still unable to cope should be gently removed and asked to find other work as the work will always involve and be subject to a war torn and violently abusive world. With the war in Iraq, in Ukraine, Hamas, and those of similar ilk around the world, there is always present need to be vigilant and the work needs to be done. This organization needs to be populated with people who can handle it. Like police work, this is not soft and cuddly work.

The second report which caught my attention was the 2025 CSIS Public Report where CSIS themselves outlined their successes for the year. It is not over revealing as the language is in very broad generalities and their limited descriptions make it difficult to discover the level of direct involvement or investigation that was undertaken by CSIS themselves. For instance in the summary portion of this report, they maintain that they conducted 100 warrants, 15 court orders, 7 assistance orders and 1 production order. These numbers are not overwhelming by any investigative measure, one mid-sized RCMP detachment would conduct that many legal undertakings in a couple of months.

In the report the authors point to a few cases with which they were involved. They point to a 19 year old male in Winnipeg who was described as displaying “nihilistic violent extremism” and the case led to terrorism related charges. It would seem that the case originated with the National Security Enforcement Section who it can be safely assumed would have got some level of intelligence from CSIS, and then the Winnipeg Police Service became involved. Hard to measure the overall input of CSIS.

Then there is the Montreal teenager who it is alleged was preparing for some style of terrorist attack, and had been posting on social media “threatening comments” and was also trying to obtain a firearm. Forty officers were involved in his arrest but the case has not made it to court yet. Then there was the woman in Montreal, accused of being a member of ISIS. Oumaima Chouay apparently left the country 10 years ago to become a member of ISIS. She was given a one day sentence, in addition to the 110 days she served in pre-trial custody.

Needless to say, the above cases are not exactly earth shattering, but there were a few other cases that CSIS clearly likes to show their effectiveness, one of which was termed operation “Hide and Stalk”.

In this case CSIS tipped the RCMP in early 2023 to a group of Canadian military individuals who were operating under the code name “Hide and Stalk”. This group was formed advocating for an anti-government militia and tactical training group and was being led by an Armed Forces Master Corporal. The tip went to the RCMP who undertook surveillance, undercover operations, and uncovered a plot to seize some property in Quebec. After an extensive investigation four individuals were arrested and charged with “facilitating a terrorist activity”, “conspiracy to forcibly seize property” and a variety of weapons offences. The Redditt forums are split on the act of it actually being an act of terrorism, that it leaned more to the survivalist mentality, but the courts will be the ultimate decider.

There were a few other stand alone investigations. In March 2026, Mathew Althorpe of Toronto, who was a member of the Telegram collective, was sentenced to 20 years for producing videos, images, publications and posts on the social messaging app Telegram, which encouraged hate against minorities, and prosecutors said was done in aid of the terrorist network the Atomwaffen Division of the Telegram collective. There was also the “dark foreigner”, the handle for Patrick Gordon McDonald who was sentenced to 10 years in 2025 for also posting and extolling videos of racist attacks on Jewish people and he too was once associated to the Atomwaffen Division which is now defunct. Or the Hydro Quebec employee who was found to be committing “economic espionage”

In reading these cases, the actual level of involvement of the CSIS agency could range from a single piece of information learned to extensive legal applications and various levels of intel. So the ability to measure the effectiveness in any of these cases cannot be seen, in fact may never be known.

The CSIS report states that since 2014 there have been 20 terrorist attacks which have resulted in 29 deaths and 60 injured. They grandiosely state it would have been “higher without their work”.

In terms of oversight. CSIS reports to the Minister of Public Safety and Emergency Preparedness, Gary Anandasangaree, who is to give them “strategic direction and policy guidance”. This Minister has a human rights legal background and there is very mixed feelings about his overall effectiveness as a Minister. Then there is the National Security and Intelligence Review Agency (NSIRA) who are there to insure “legality and propriety”. There is in addition the National Security and Intelligence Committee of Parliamentarians (NSICOP) made up of MP’s and Senators. This latter group are described as there to act as an “independent, quasi judicial oversight body” and are in fact led by a retired Superior court judge. Their stated job is to have up front oversight by “reviewing and approving”. One does get the impression that a speedy decision in times of a national threat may be out of the question with the levels of bureaucracy that are currently in place, but nevertheless they are there. You just don’t get to see what they are dealing with or any decisions coming out of these bodies of government. I didn’t mention that there is also the Integrated Threat Assessment Center (ITAC), and there is also a group that measures the “Threat to Public Officials” and a group that is there to assess the “National Terrorism Threat Levels.”

In case you are interested this last group says that we are now at “Medium” threat level; which means that there is a “realistic possibility” of a terrorist threat. Feel better, because I am not so sure we have determined whether CSIS is a viable or effective organization? All we really know is that some people inside the organization don’t think you should apply for a job.